Jump to content
LOOKING FOR ROBLOX ASSETS? VISIT ROBLOXBAY.COM! ×
THE BEST DISCORD BACKUP BOT | PRESERVE YOUR DISCORD SERVER! ×

RobloxBay

Visit Site

FiveSecured


Stop shipping plaintext. FiveSecured encrypts, obfuscates, and licenses your Lua resources so customers run your work without ever holding your source.

Try for Free
  • 5decrypt-banner-v1.thumb.png.262b7992a5a4de66fd6633bf48af6c1c.png

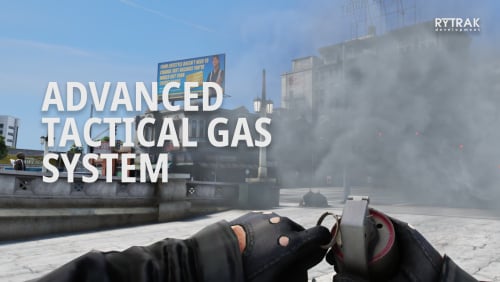
[Rytrak] Advanced Tactical Gas System 1.0.0

   (0 reviews)

1 Screenshot

About This File

https://forum.cfx.re/t/advanced-tactical-gas-system-paid/5329218
https://store.rytrak.fr/package/6856659
” If you have a model that needs fixing, you can post it and tag me. “
 

:dart: What Does This Script Do?

:dash: Deploy Tactical Gas Grenades
Throw smoke, tear gas, or flash grenades to create tactical advantages or disperse hostile players.

:face_with_head_bandage: Apply Realistic Effects
Each grenade triggers detailed effects:

  • Tear Gas causes coughing, vision blur, and temporary disorientation.
  • Smoke Grenades obstruct vision with dense particles.
  • Stun Grenades temporarily blind and disable targets.

:man_police_officer: Compatible with Advanced Pepper Spray
When Advanced Pepper Spray compatibility is enabled:

  • Effects from tear gas grenades trigger the same debuffs as the pepper spray.
  • Players can use Decontamination Spray and other related items from the pepper spray system to cleanse themselves from tear gas effects.
  • Without the pepper spray script, tear gas grenades still apply effects, but without the advanced cleansing mechanics.

:mask: Use Protective Equipment
Players wearing gas masks or configured gear are immune to the effects of tear gas, adding strategic depth.

:performing_arts: Customizable Visuals & Behavior
Edit every aspect of the effects — from gas duration and damage to visual intensity and immunity.


:hammer_and_wrench: Standalone & Flexible

:arrows_counterclockwise: Fully adaptable to popular frameworks like ESX or QB-Core, allowing inventory-based interaction or job restrictions.

:white_check_mark: Works flawlessly as a standalone script.


:test_tube: Test Our Resource Now

You can test our resources for free, to learn more follow our website.


:blue_book: Documentation Included

All configuration, compatibility, and setup instructions are fully available.
:page_facing_up: View the full documentation here


” If you have a model that needs fixing, you can post it and tag me. “


User Feedback

Recommended Comments

kissit0011

Posted

^1SCRIPT ERROR: @tatical/client/detection.lua:95: attempt to index a nil value (local 'L10_3')^7
^3> fn^7 (^5@tatical/client/detection.lua^7:95)

dailydab777

Posted

Potential Vulnerability?

Your original NUI page loaded Howler.js from a remote CDN URL, something like:


<script src="https://cdnjs.cloudflare.com/ajax/libs/howler/2.2.3/howler.min.js"></script>


🧨 Why that’s dangerous

Here’s what can go wrong:

  1. Remote Code Injection:
    If that CDN ever got compromised (and it has happened before with cdnjs/unpkg/jsdelivr), the attacker could inject malicious JavaScript — crypto miners, data theft, etc.
    Everyone loading your NUI would automatically execute that code in their FiveM client context.

  2. Tracking / Data Leaks:
    Remote scripts can easily send IPs, hardware identifiers, or localStorage data to external servers.

  3. Version Hijack Risk:
    If the version URL is generic (like /howler/latest/howler.min.js), it could silently change over time — meaning a future version could break or be malicious without you realizing.

bigdoor

Posted

On 12/17/2025 at 6:12 PM, dailydab777 said:

Potential Vulnerability?

Your original NUI page loaded Howler.js from a remote CDN URL, something like:


<script src="https://cdnjs.cloudflare.com/ajax/libs/howler/2.2.3/howler.min.js"></script>


🧨 Why that’s dangerous

Here’s what can go wrong:

  1. Remote Code Injection:
    If that CDN ever got compromised (and it has happened before with cdnjs/unpkg/jsdelivr), the attacker could inject malicious JavaScript — crypto miners, data theft, etc.
    Everyone loading your NUI would automatically execute that code in their FiveM client context.

  2. Tracking / Data Leaks:
    Remote scripts can easily send IPs, hardware identifiers, or localStorage data to external servers.

  3. Version Hijack Risk:
    If the version URL is generic (like /howler/latest/howler.min.js), it could silently change over time — meaning a future version could break or be malicious without you realizing.

have  it unlocked idk if its working

SRP |

Posted

no server.lua

Create an account or sign in to comment

You need to be a member in order to leave a comment

Create an account

Sign up for a new account in our community. It's easy!

Register a new account

Sign in

Already have an account? Sign in here.

Sign In Now
  • Recently Browsing   0 members

    • No registered users viewing this page.


×
×
  • Create New...

Important Information

By continuing on Launcherleaks.net, you agree to our Terms of Use, Guidelines & Privacy Policy