


tatertotgod
-
Posts
1 -
Joined
-
Last visited
About tatertotgod
tatertotgod's Achievements
Newbie (1/17)
0
Reputation
-
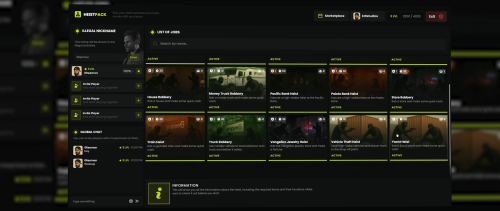 FiveM Resource Warning: Suspicious Backdoor Code Found I recently inspected two FiveM resource ZIPs: 0r-heistpack.zip 0r_lib.zip The exact copies I inspected contain concealed code that can download JavaScript from outside servers and execute it on the FiveM server/client environment. I would not install or run these copies on a production server. What was found? 🔴 0r-heistpack The resource contains a file: client/bootstrap.js that extracts hidden Base64-encoded JavaScript from its own UI files and executes it using: new Function(code)(); The decoded code reaches out to an external domain: hzdh.4rf6.com and can download additional JavaScript. That downloaded content is then executed. There are also files pretending to be fonts, such as: Arial.ttf that are not normal font files and contain obfuscated remote URLs. The Lua code also contains an intentionally obscured reference to Lua's load() function: _G[string.char(108,111,97,100)] which resolves to: _G["load"] That is a common way of hiding dynamic code execution from a casual code review. The archive also contains files/comments related to bypassing the resource's original licensing system, including names such as: license-patch.js index-patched.js index-license-free.js This strongly suggests the copy has been modified. 🔴 0r_lib This one is even more concerning. Obfuscated JavaScript decodes into code that connects to external servers including: ebk.9ns1.com mm.9ns1.com It attempts to download remote JavaScript payloads from addresses similar to: /zXeAHJJ /zXeAHJJgg /zXeAHJJcfxre The response is then executed using JavaScript eval(). In simple terms, the behavior is: Connect to outside server ↓ Download JavaScript ↓ Execute downloaded code That means the person controlling the remote website can potentially change what gets executed without modifying the FiveM resource ZIP itself. There is also another fake font file: Roboto.ttf containing an obfuscated external URL rather than normal font data. Why this matters A legitimate update checker normally does something like: Check current version ↓ Compare version number ↓ Tell administrator an update exists What these files do is fundamentally different: Download executable code ↓ eval() / new Function() ↓ Run it That creates a remote-code execution mechanism. Depending on what the downloaded payload does, this could potentially be used to access things available to the server process, interfere with resources, steal configuration/secrets, or download additional code. Indicators to search for If you have used these resource copies, search your FiveM server files for strings like: 9ns1.com 4rf6.com jgir jgirJJ zXeAHJJ zXeAHJJgg zXeAHJJcfxre miausass Also watch for patterns such as: eval(data) new Function(code) and Lua obfuscation resembling: _G[string.char(108,111,97,100)] If you've already run them I would recommend: Stop the affected resources. Remove the questionable copies of 0r-heistpack and 0r_lib. Search the rest of your server for the domains and loader patterns above. Inspect any other resources downloaded from the same source. Rotate sensitive credentials the server process could access. Check Discord webhooks, API tokens, database accounts, FiveM configuration, and other secrets. Restore from a known-clean backup if you discover additional modifications. Important clarification I am not claiming that every official/original version of these resources is malicious. This report applies specifically to the two ZIP files that were inspected. They could have been modified, cracked, repacked, redistributed, or infected after leaving the original developer. So the correct warning is: The copies inspected contain concealed remote-code execution behavior. Verify the source and integrity of your own files before using them. Bottom line Both inspected packages contain behavior that should never be hidden inside an ordinary FiveM heist/library resource. 0r-heistpack.zip 🔴 UNSAFE COPY 0r_lib.zip 🔴 UNSAFE COPY The biggest red flag is simple: Remote JavaScript is downloaded and executed using eval() / new Function(). For a FiveM production server, that's enough reason to quarantine the files immediately. 🚨
